Descrizione
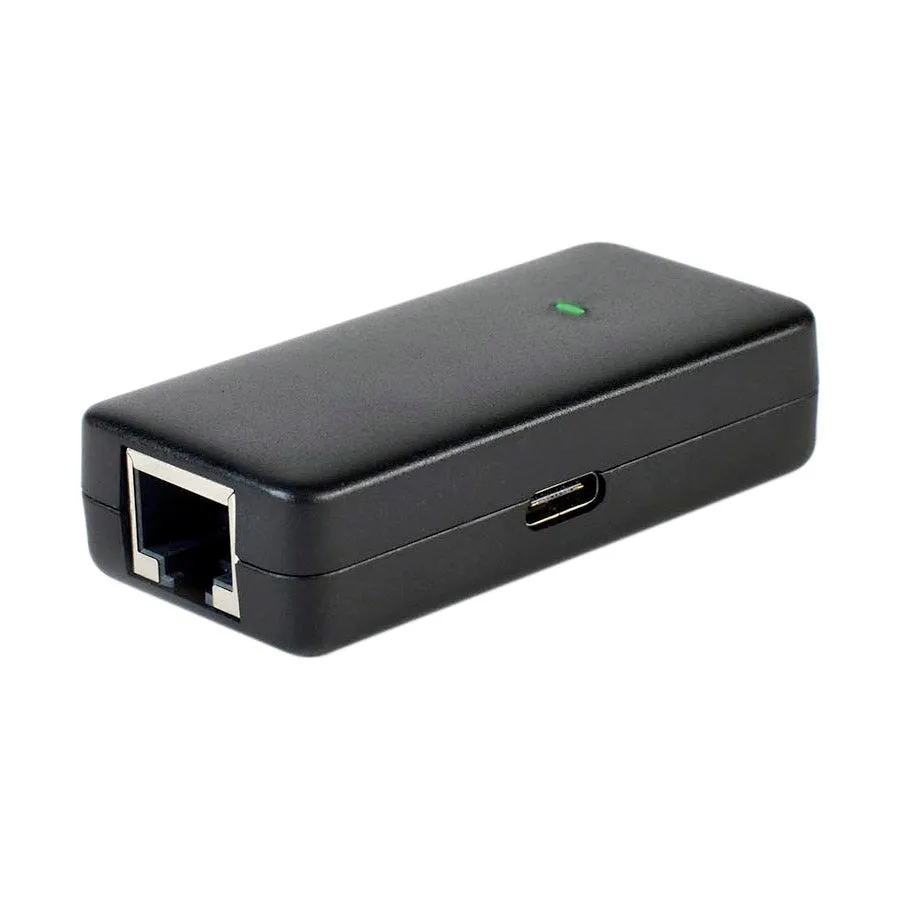
The Hak5 Plunder Bug places an Ethernet connection between two devices and mirrors traffic to its USB-C tap port for authorised monitoring and assessment. It can support passive packet capture or active testing when used with suitable analysis tools and approved network access. RedKit Labs is an authorised Hak5 reseller.
Key features
- Inline LAN tap for wired Ethernet connections
- Mirrors traffic between the two RJ45 Ethernet ports to the USB-C tap port
- Supports passive mode, which mutes the tap port to prevent downstream transmission
- Supports active mode for bidirectional network access during authorised assessments
- USB-C connection for tapping and power
- Cross-platform connection scripts for Windows, macOS and Linux
- Works with network analysis tools such as Wireshark and tcpdump
Technical details
- Auto-negotiating 10/100 Base-T Fast Ethernet
- ASIX AX88772C USB Ethernet chipset
- USB-C tap and power port
- 5 V supply
- Power draw: 20 to 300 mA
Compatibility and setup
Connect the Plunder Bug to a computer with a USB-C cable, then use two Ethernet cables to place it inline between the devices under assessment. The host computer detects an ASIX AX88772C USB Ethernet interface. Hak5 provides connection and mode-switching scripts for Windows, macOS and Linux. A compatible USB-C cable and two Ethernet cables are required.
Buying in the UK and EU
RedKit Labs offers this Hak5 device for buyers in the UK and EU, with prices displayed in GBP, EUR or USD and VAT handled at checkout. Use it only on networks where testing and packet capture are explicitly authorised.


Recensioni
Ancora non ci sono recensioni.